
 Dan
2021. What an interesting year. With the world turned upside down by a pandemic that seemingly had its sights set on...

Is Your Nonstop System Ready for It’s Next Audit?
CSP
 Andy Vasey
Is Your Nonstop System
Ready for It’s Next Audit?
 Security is the foundation of your IT infrastructure. Most organizations running Nonstop systems have been around for a long time and their IT Infrastructures were built long ago.
As with any infrastructure, wear and tear creates vulnerabilities. Organizations must constantly maintain their systems to identify cracks in the foundation. If those vulnerabilities are left unattended, they can cause severe structural damage.
Similarly, implementing solutions to identify vulnerabilities will help strengthen your overall security posture.
Having these solutions in place will help to ensure you can confidently meet requests from auditors. Identifying vulnerabilities in your system and taking appropriate remedial actions to help prevent security breaches and data loss is an important part of an organization’s Digital Resilience strategy.
Threat actors can exploit security exposures and gain access to sensitive data, cause damage to the network, and deny access to authorized users. Vulnerability Management is key to mitigating risks and improving your security posture.
An effective operational risk management framework includes regularly reviewed and updated policies and procedures, a risk classification system that includes categories of risks related to people, inadequate internal processes and systems, and external events, and assessment and monitoring tools to evaluate risks and controls.
From an organizational standpoint, operational risk management requires several collaborative defensive systems to properly assess and manage risk, including vulnerability scanning, user validation, and threat detection.
Identify & Manage Risk
Operational risk management is centered on the assurance that all vulnerabilities associated with business activities are properly identified and understood, that the associated risks are formally assessed and quantified, and that there is a structured process in place for enacting the decisions made by leadership functions to manage vulnerabilities and the associated risks.
 There are multiple regulatory frameworks focused on digital operational resilience and risk management. Organizations must now prove their Digital Operational Resilience. ICT risk management is a key pillar of these frameworks. A comprehensive risk management framework for ICT systems includes policies, procedures, regular assessments and programs.
Ensuring users can perform their routine tasks without reducing efficiency and effectiveness, while keeping systems and data secure and compliant, is the key to managing risk effectively.
We cannot eliminate all risk, but we can mitigate and manage vulnerabilities and reduce our threat surface.
How can Monitoring Nonstop-Connected Hardware Devices Strengthen Digital Operational Resilience?
Monitoring hardware devices is crucial for minimizing system downtime and ensuring optimal performance, efficiency, and security. It can provide real-time insights into hardware health, detect issues before they escalate, prevent data loss, and inform proactive maintenance and upgrade decisions.
 Monitoring also improves insight and visibility into the Hardware Security Module (HSM), facilitating more effective management and troubleshooting of any issues.
Regulatory compliance is no small undertaking. It requires the right partner to ensure not only compliance but also an environment of readiness and continuous improvement.
How can you Effectively Monitor Nonstop-Connected Hardware Devices?
CSP has been an innovator in NonStop security for over thirty years and understands the complex security challenges facing the NonStop platform. No organization is immune to threats. CSP understands enterprises require insight and visibility into the Hardware Security module, so we developed CSP Syslog Receiver to assist with monitoring of devices connected to Nonstop environment.
HSMs and ESKMs handling encryption keys for payment transactions are often invisible to Nonstop teams.
Syslog Receiver captures HSM and ESKM messages in real time and forwards them to EMS and SIEM, providing visibility into hardware status, upgrade failures, and power events. This solution relates to DORA’s third-party infrastructure requirements.
CSP Syslog Receiver for Nonstop servers is an OSS Gateway tool that receives syslog messages from Hardware Security Modules (via TCP/IP or UDP),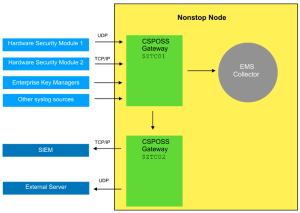 and forwards to EMS collectors and SIEM. This solution delivers improved insight and visibility into the Hardware Security module (HSM), facilitating more effective management and troubleshooting.
Get a live view and detailed insights into the HSM status during upgrades. Having the Syslog receiver running during an HSM upgrade gives a much better view of any upgrade issues or failures when they happen, as compared to HSM log files that are not visible in real time.
The installation and setup are very quick, and the product is simple to use.
Supports Multiple Syslog Sources
In addition to Hardware Security Modules, messages from various other syslog sources can be sent to EMS, providing increased visibility and awareness of the devices connected to Nonstop environment.
CSP Syslog Receiver improves insight into the Hardware Security Module, increases visibility and awareness of devices connected to the Nonstop environment, and can receive critical messages regarding hardware failure/power failure. CSP Syslog Receiver now also supports Enterprise Security Key Managers (ESKM’s).Key Features:
- OSS process managed by config file (YAML format)
- Supports TCP/IP and UDP protocols
- Specify a dedicated EMS collector for Syslog messages.
- Supports multiple syslog sources
- Support for Enterprise Security Key Managers
- Forward Syslog messages to SIEM (e.g. Splunk).
- Ability to run as a Pathway process
- Quick installation and setup
- Simple to use
- No GUI to install
When it comes to securing your Nonstop Systems, you have options. For more information about CSP Syslog Receiver, visit CSPsecurity.com.
CSP – The Superior Choice in NonStop Security
The CSP Team
+1(905) 568 –8900
